There is a moment every safety manager hopes to avoid but should always prepare for: an incident has happened, and someone — an inspector, a lawyer, a commissioner at a hearing — is going through your records line by line, deciding whether your organisation did what a reasonable employer should have done. In that moment, the quality of your safety work matters far less than the quality of your evidence of that work.
A defensible safety record is one that can withstand that scrutiny. It is not about having more paper. It is about having records that are contemporaneous, complete, consistent and connected. This piece unpacks what that means in practice, particularly for operations governed by the OHS Act and the Mine Health and Safety Act.
Why records become the whole case
Under South African law, an employer’s duties are largely about reasonable, proactive care. Section 37(2) of the OHS Act, for instance, turns on whether you took reasonable precautions and exercised due diligence to prevent an employee’s act or omission. You cannot prove diligence with good intentions. You prove it with records: the risk assessment that identified the hazard, the control you put in place, the training that showed the worker understood it, the inspection that confirmed it was working.
When those records exist and hang together, they tell a coherent story of a system doing its job. When they are missing, contradictory or reconstructed after the fact, the absence itself becomes the finding — and a decision-maker is left to assume the work was not done.
The four properties of a defensible record
Contemporaneous
The single most important quality. A record made at the time of the work — timestamped, attributed to the person who did it — carries weight. A record reconstructed a week later, or worse, produced only once an incident is under investigation, invites the obvious question: was this created to describe what happened, or to defend it? Capture at the point of work is not a convenience feature; it is what makes the record credible.
Complete
Gaps are where scrutiny concentrates. If you can produce eleven of the last twelve monthly inspections for a site, the missing one is the one everybody will ask about. A defensible record is unbroken — the routine was followed, and the following is documented, without holes.
Consistent
If your procedure says inspections happen weekly and your records show them happening sporadically, the contradiction undermines both. Defensibility depends on your documented system and your actual records telling the same story. This is why a controlled document library — where the current procedure is the one on the floor, and old versions are retired — matters as much as the records themselves.
Connected
Individual records are useful; linked records are persuasive. A hazard identified in a risk assessment, traced to a control, verified in an inspection, and — where it failed — driving a corrective action that was closed and checked. That chain demonstrates a functioning management system. Disconnected records demonstrate only activity.
Where defensible records break down
In most estates the failure is not laziness; it is fragmentation. Records live in different places — a WhatsApp photo here, a signed paper form there, a spreadsheet on someone’s laptop — with no way to assemble them into a chain when it counts. The information exists, but not as evidence.
Common weak points to check honestly:
- Attribution. Can you show who did each inspection and check, not just that it was done?
- Edit history. If a record can be changed silently after the fact, its evidential value is weak. Defensible systems keep an audit trail of changes.
- Retrievability. A record you cannot produce quickly is, in a hearing, effectively a record you do not have.
- Findings without close-out. A logged hazard with no evidence of action is worse than no record — it proves you knew and did nothing.
Build it in, do not bolt it on
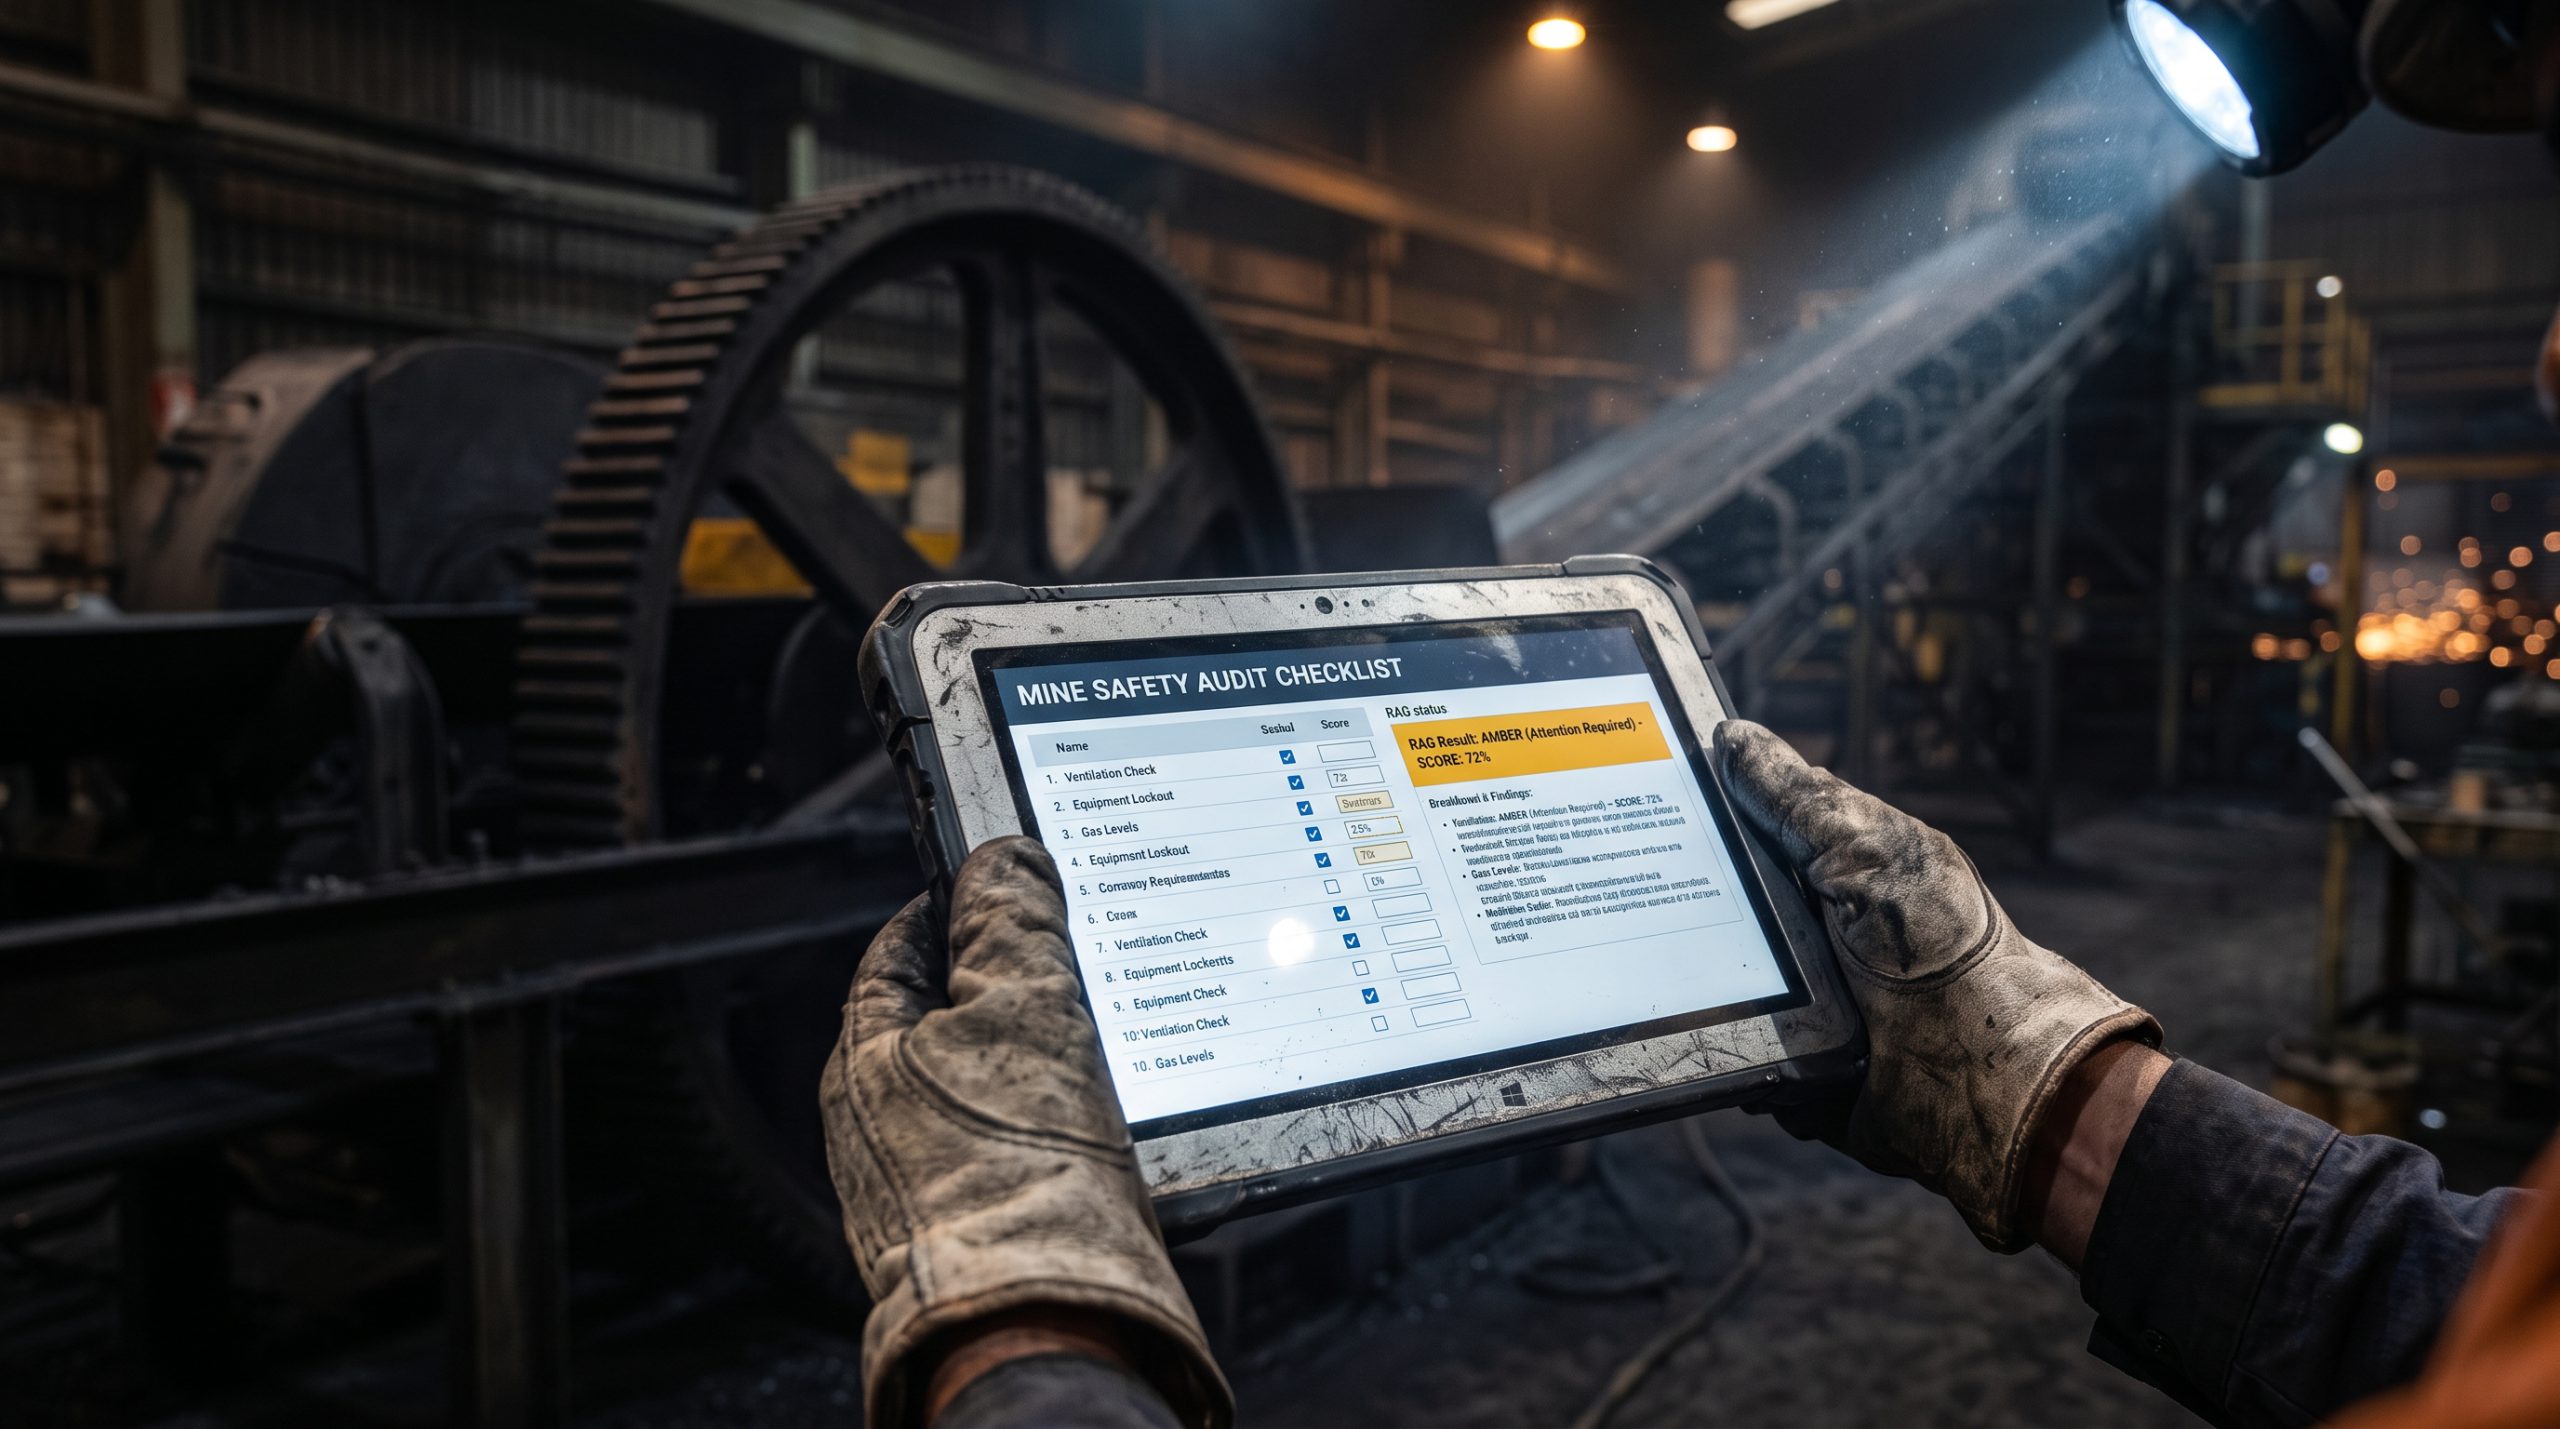
Defensibility cannot be manufactured after an incident. It is the by-product of running a disciplined system every day: standardised inspections captured at the point of work, findings routed to tracked actions, a single source of truth for procedures, and periodic reviews that catch gaps early. If those disciplines are running, the defensible record assembles itself. For mining operations under the MHSA, the same logic applies with even less tolerance for gaps — see how it plays out for mining teams.
Key takeaway
A defensible safety record is contemporaneous, complete, consistent and connected. You cannot build it after an incident — it is the residue of running a disciplined system every day, with records captured at the point of work, attributed to people, and linked into a chain that proves your system actually functioned.
A worthwhile exercise, before you ever need it, is to pick one recent incident or hazard and see whether you can assemble the full chain of evidence around it today. If the chain has broken links, that is where to start. We are happy to talk through how a single connected record set holds up under scrutiny — book a demo when it helps.